

North Korea Hacks and Steals Cryptocurrency to Fund WMD Development
Lee Donghoon
Contributing editor of Tech Focus
The recent incident of the North Korean Lazarus Group stealing cryptocurrency at an unprecedented scale shocked the world. This is also a case that clearly shows North Korea’s cyber warfare capabilities.
In this article, we will look at their cyber warfare capabilities, characteristics, and countermeasures, focusing on this theft and subsequent incidents.
On February 21, Bybit, the world’s second largest cryptocurrency exchange, suffered the largest hacking damage ever. The hack by North Korea’s Lazarus Group resulted in the theft of $1.46 billion (about 2.1 trillion won) worth of cryptocurrency.
The hackers stole Ethereum (ETH) and Ethereum-based cryptocurrencies, and the stolen assets were converted into Bitcoin (BTC) through a money laundering process.
As a result, North Korea suddenly came into possession of 13,562 BTC, becoming the third largest country in Bitcoin holdings. The Bitcoin acquired in this way is used as funds for North Korea’s WMD development.
The reason North Korea is desperate to steal cryptocurrencies is because they are all virtual assets that do not have any physical form, so they can be stolen with sufficient hacking skills, and there is no other way to secure a source of funds due to the international sanctions.
This coin theft occurred during the process of transferring assets from a cold wallet to a hot wallet. Exchanges usually use an offline wallet (cold wallet) to increase security and an online wallet (hot wallet) with fast deposits and withdrawals.
Cold wallets are safe from online hacking because they store cryptocurrencies while not connected to the Internet. Exchanges usually store about 80% of the assets entrusted by users in cold wallets that are relatively secure, and the rest in hot wallets with fast deposits and withdrawals. Hackers mainly target when funds are transferred between wallets.
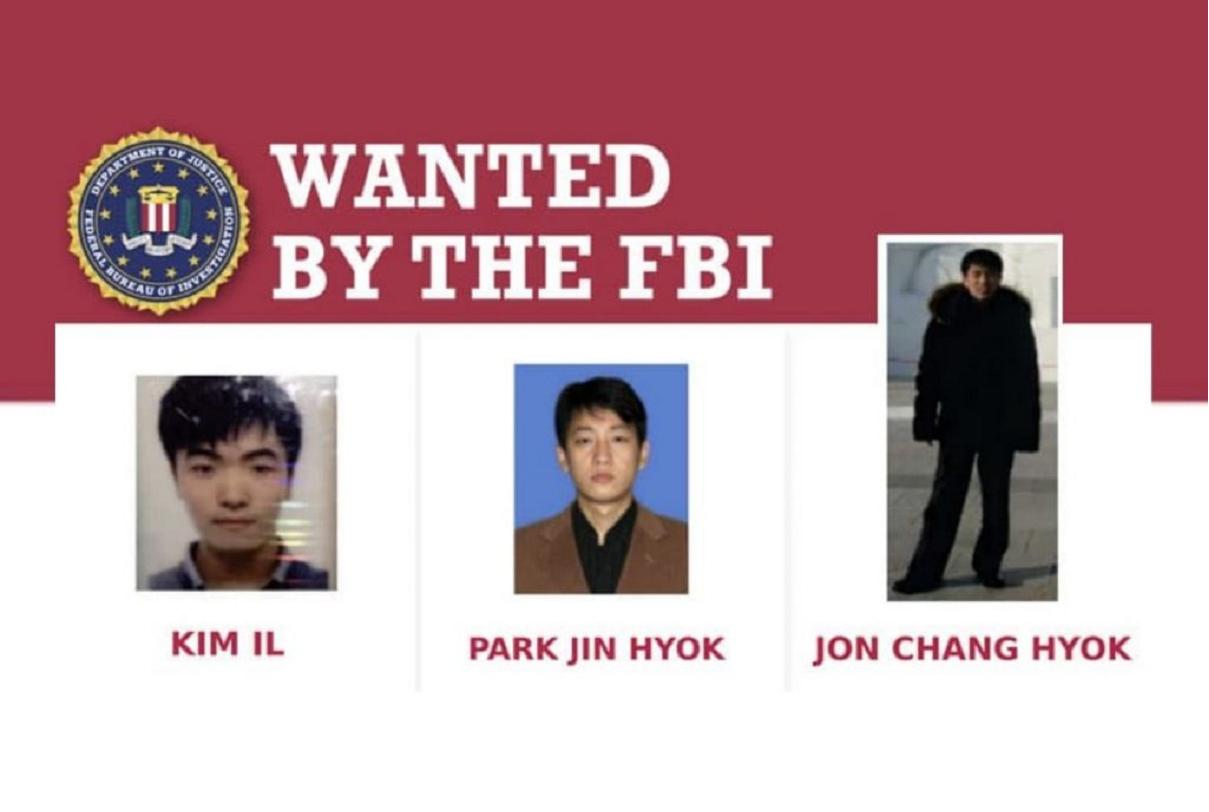
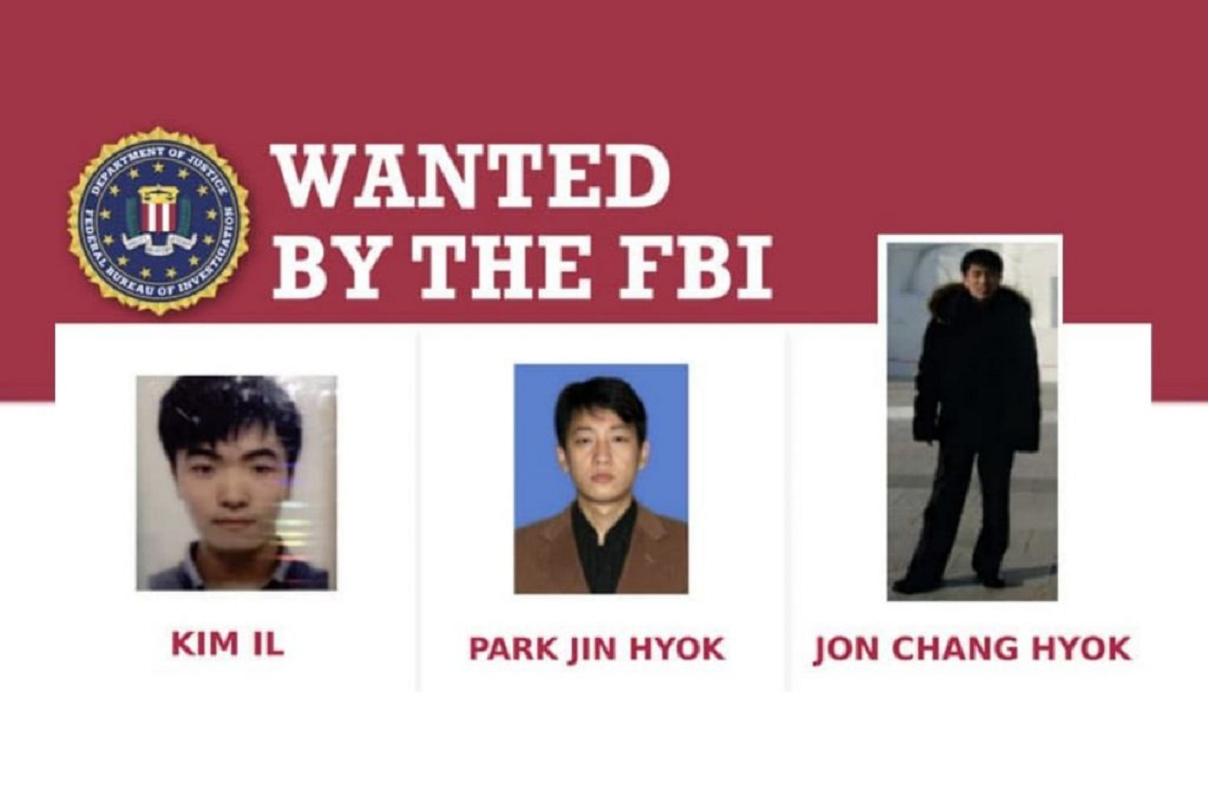
Wanted poster for North Korean hackers distributed by the FBI
North Korean hackers have already shown their prowess in cryptocurrency hacking. The amount stolen by North Korean hackers increased from $660.5 million (KRW 955.2 billion) in 2023 to $1.34 billion (KRW 1.9376 trillion) in 2024, which is a 102.88% increase from the previous year.
It accounts for a whopping 61% of the total cryptocurrency hacking damage last year. The number of cryptocurrency hacking incidents they committed also more than doubled from 20 to 47, but the problem is that the frequency of attacks is increasing as well as their scale.
The average time it takes to successfully attack is steadily decreasing, and attacks worth more than $100 million (KRW 145 billion) are much more frequent than before.
North Korean hackers use specialized money laundering techniques such as mixers and bridges to cash out the stolen funds. A mixer is a technology that splits and mixes cryptocurrencies to obscure the source of the funds.
It was created for the purpose of anonymizing most of the transaction information for customers who want to strengthen the anonymity and decentralization of their assets, but it is currently being abused to hide the source of funds and the remittance destination.
The bridge is a function that allows transactions between different types of cryptocurrencies, but it is being abused for the purpose of changing the stolen cryptocurrencies into other cryptocurrencies to make it difficult to trace the funds.
What is more serious about North Korea's cryptocurrency theft and money laundering is that it uses overseas infrastructure as well as North Korea.
In particular, it was revealed that the US currency exchange network THOR Chain was used to launder $1.2 billion, which is 85% of the cryptocurrency stolen from Bybit in February. Despite pressure from the US government, THOR Chain is not blocking North Korea-related transactions.
According to blockchain security researchers who told CoinDesk, a US journal specializing in the field, this is because the main developers and validators of THOR Chain received a considerable fee from the transaction. It is estimated to be over $12 million.
Chinese crime syndicate is also involved in North Korea’s cryptocurrency money laundering. According to research by TRM Labs (hereinafter referred to as TRM), a U.S. blockchain research institute, the black market financial network operated by Chinese crime syndicate is providing critical assistance to North Korea and other rogue states and criminal organizations in exchanging cryptocurrency. Ari Redboard,
TRM’s chief international policy officer, pointed out that U.S. law enforcement agencies have failed to stop their activities until now because they have not faced this clear fact.
Nick Carlson, a former FBI analyst and investigator for TRM, said, “North Korea laundered the stolen Ethereum and converted it into Bitcoin, making it difficult to track,” and revealed that this money laundering was not done directly by North Korea, but by third parties such as THOR Chain and the Chinese black market financial network.
He also pointed out that even a small portion of the money laundering capabilities of the Chinese black market financial network were enough to satisfy North Korea’s needs.
According to TRM's research, this powerful Chinese black market financial network is operated by violent organizations such as the Black Society, and various criminal organizations exchange cryptocurrencies deposited by them for legal tender.
This is because the government's surveillance of China's institutional banks is very strict, making it difficult for criminal organizations to use them. This is also why people who want to evade taxes while conducting large-scale transactions often use this black market financial network.
North Korea is also directly securing overseas bases. According to Reuters on the 24th, it was revealed that North Korean hackers set up front companies in the United States and used them as bases to spread malware to developers.
According to an investigation by Silent Push, a U.S. cybersecurity company, Blocknovas, Softglide, and Angeloper Agency were among the front companies established by North Korea. All of them use non-existent representatives and fake addresses.
However, except for Angeloper Agency, all of them are officially registered businesses with the U.S. government, making it a very rare form of attack. North Korean hackers posted fake job advertisements in the names of these companies, conducted remote interviews with developers who responded to the advertisements, and sprayed them with malware.
This malware stole not only the developers’ cryptocurrencies but also their passwords and credentials, helping the North Korean hackers carry out subsequent crimes. The operators of these front companies were small groups under the North Korean hacking group Lazarus, which became famous for the Bybit hack in February.
Tracking and eradicating the funding sources for North Korea's WMD development will not be easy in the future due to North Korean hackers who use cutting-edge IT technology to fool the world, as well as third-country citizens who turn a blind eye to this for economic gain.
In conclusion, it is essential to establish an international cooperation system that goes beyond individual responses to North Korea's hacking. To this end, governments and companies of each country should establish a closer information sharing system and introduce a surveillance system that can detect suspicious transactions in real time.
In addition, regulations should be strengthened to prevent cryptocurrencies stolen through hacking from being illegally distributed through money laundering. It is also advisable for general users to thoroughly manage their personal security and use platforms with verified security.
When governments, companies, and individuals cooperate to build a multi-layered defense network, they will be able to maintain market trust.
-
PREV [News&Issue]
-
NEXT [Feature Article]